
Workload identity federation
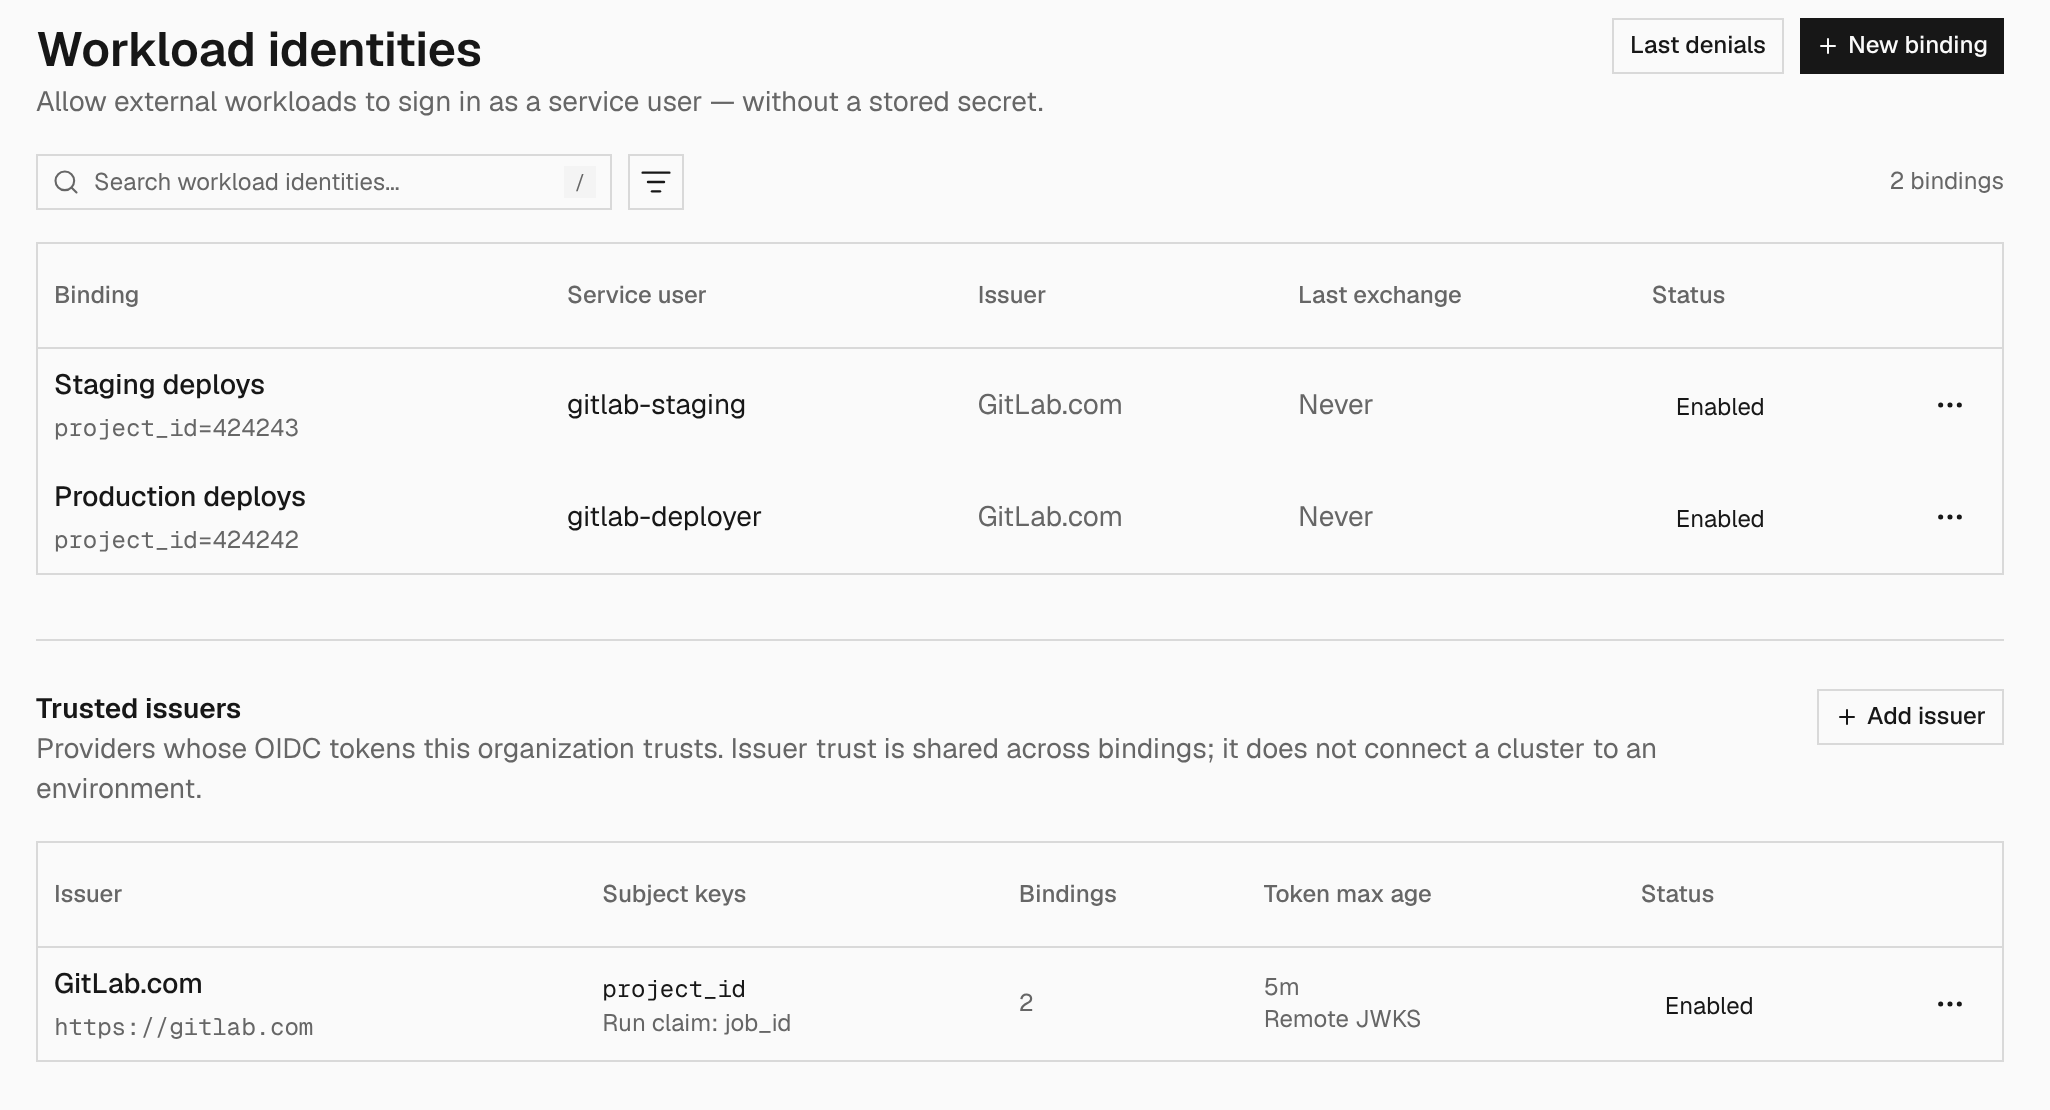
CI jobs, cloud workloads, and Kubernetes pods can now authenticate to Ryvn with their own OIDC tokens, so there's no Ryvn client secret to store or rotate. You trust an OIDC issuer such as GitLab CI and bind specific token claims to a service user, and the Ryvn CLI exchanges the workload's token for a short-lived Ryvn credential.