
Keyless CI authentication
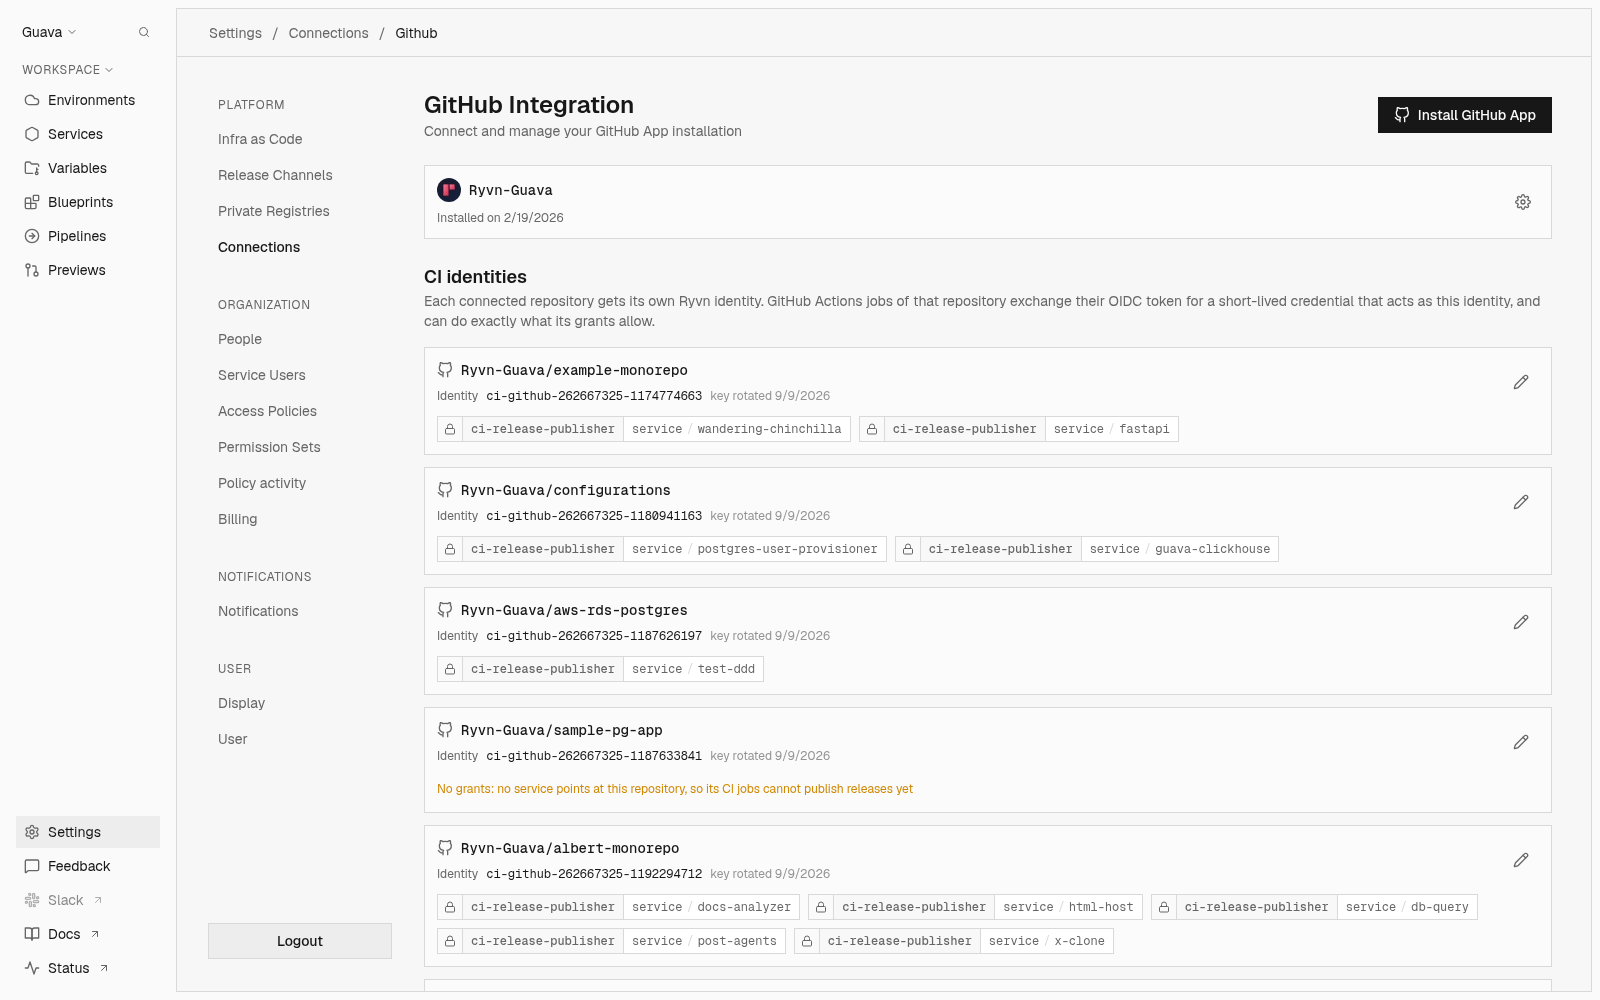
Your GitHub Actions workflows now authenticate to Ryvn with the job's own GitHub identity instead of a client secret stored in the repository: the job requests its OIDC token with id-token: write, and the Ryvn CLI exchanges it for a short-lived credential scoped to publishing releases for the services that repository owns. You have nothing to store, nothing to rotate, and nothing that keeps working after a leak, and each connected repository gets its own CI identity whose grants you can review under Settings > Connections > GitHub.