
Egress network policies
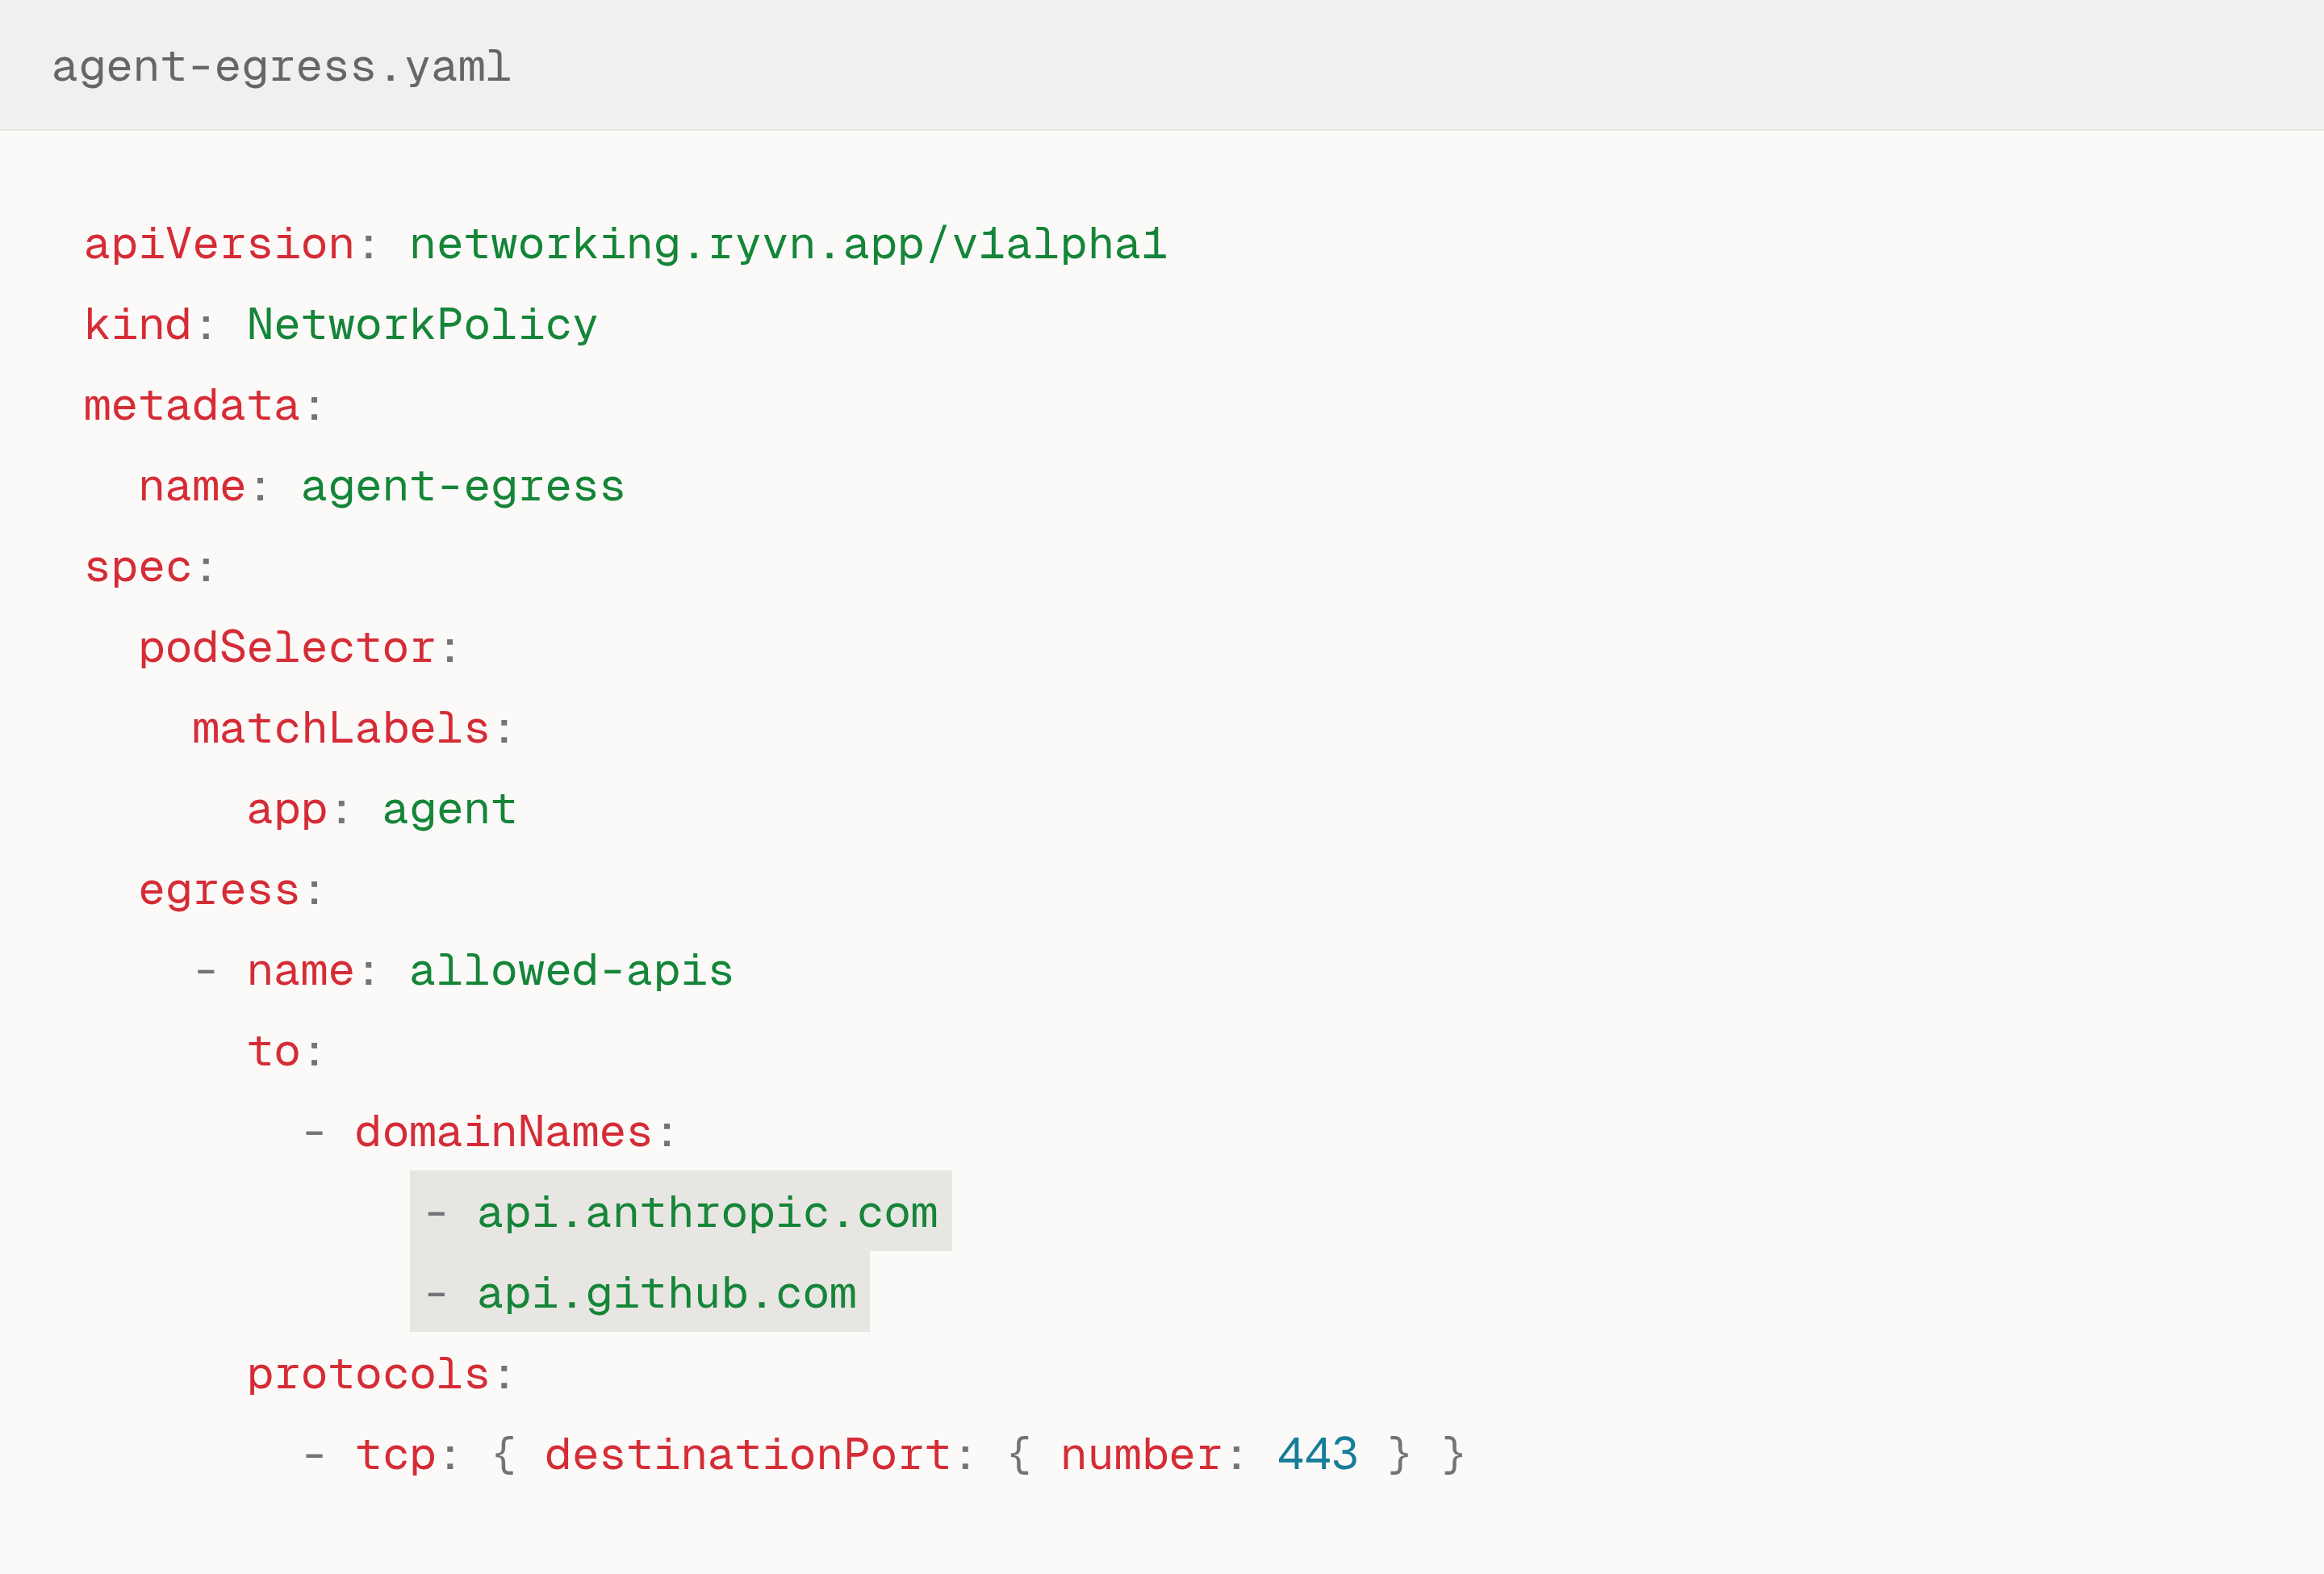
Every new environment Ryvn provisions on AWS, Azure and Google Cloud now uses Cilium as its default network layer (CNI). A network policy now works the same way on all three clouds.
With network policies, you choose what each workload can reach and block everything else. A policy can allow domain names such as api.anthropic.com, IP ranges, or other workloads in the cluster. For example, you can limit an AI agent to its model API, or a service in a customer's cloud to the APIs it depends on. Run untrusted agents in an isolated namespace so they also can't reach workload identity or the Kubernetes API.